Found the cause: greenhouse-controller's firmware channel changed from stable to nightly at 01:48 UTC, 12 minutes before greenhouse-controller first failed
Put greenhouse-controller back to stable, its last good setting
greenhouse-controller is back on its last good setting
greenhouse-controller · firmware channel
stable
Asked
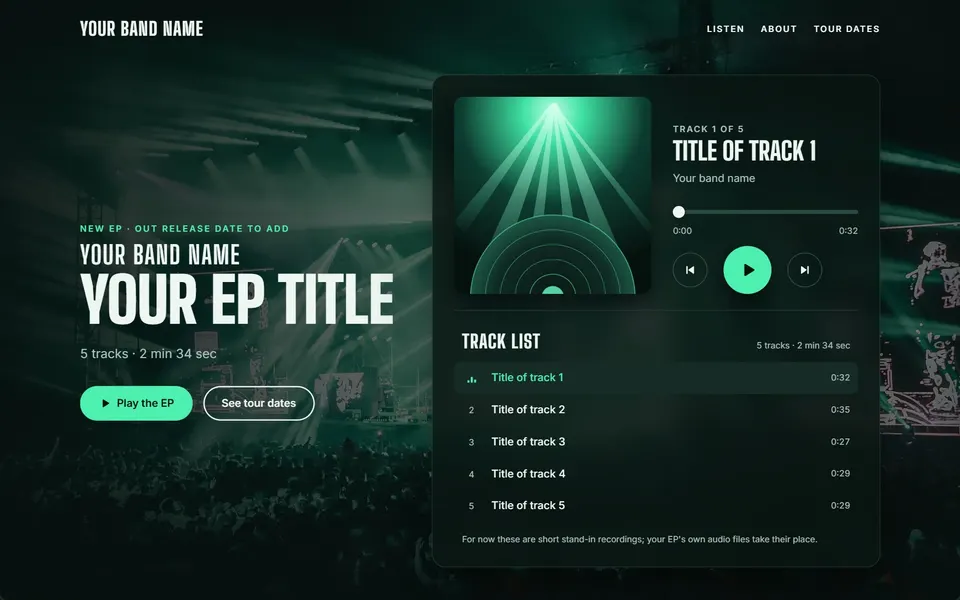
“A music player page for a band's new EP with track list, play and pause, a progress bar and tour dates”
Found it: port 1 was shut by the switch’s own loop protection, a second cable closing a loop
Said which cable to pull, then turned the port back on the moment the loop was gone
The link is back up and the router answers again
Port 1 – the link to the router
Shut → Back on
Xovris watches the public signals an attacker leaves on your domain – certificates issued for your names, the signing that protects your domain’s address book (DNSSEC) breaking, certificate rules that change – reads your Cyber Essentials readiness from your real computers and accounts, and tells you which ones need you.
Checks devices and software against the holes attackers use now
Switches a leaked key off for you
Technical detail
Sign-insPassword-only sign-ins found, and an affected account locked down in one step · Require a passkey for everyone in your workspace
Holes in devicesEvery device you connect, checked for known security holes, worst first · The software on your computers checked every day against the vulnerabilities attackers are using now – and the one upgrade that closes them, done for you
Attack paths in codeA broken build fixed and proven before CI runs again, and every change checked for attack paths
Leaked keysKnow whether a leaked API key is switched off for you · Your keys never pass through the AI · Your keys stay sealed, every step stays inside what you allowed, and nothing Xovris reads can tell it to act
Lookalike domainsA lookalike site's abuse report is filed by Xovris the moment it can be, never left to you · A lookalike page or a forged link never becomes a fact about your incident
Email spoofingThe free website check now reads security headers, email, DNS, uptime worldwide, links, cookies and more
BreachesYour email addresses, domain and brand watched for breaches and lookalikes, and the response done for you · Four more free checks: blocklists, security headers, Cyber Essentials readiness and leaked passwords · “Is this a scam?” answered with the reasons – and what to do next if you already clicked, typed a password or paid
Each watch lit by the features that ship for it today, from the release record
01
What Xovris readon its own domain.
xovris.ai is served from Cloudflare, Inc., keeps its DNS on Cloudflare and keeps its email on Microsoft 365. Everything Xovris could read on xovris.ai answers as it should – none of 11 readings is wrong.
Security on xovris.ai23:05:28 UTC
Certificate
Fine
Valid until 31 December 2026 – 42 days left.
Security headers
Fine
Graded A+ for the headers that tell browsers how to protect your visitors.
Signed address book (DNSSEC)
Fine
Signed and validated: forged answers about where this domain lives are rejected.
Certificate rules
Fine
Only the certificate authorities named here may issue its certificates.
Lookalike addresses
Fine
Similar names registered by someone: 5 of the 40 likeliest, 2 of them taking email. That is ordinary – most similar names are someone else’s own. This check reads only that they exist; when Xovris watches your address it opens each one and raises only a name that imitates yours.
XovrisOn its own
What Xovris sees on a domain, line by line.
The values behind each answer, exactly as they were recorded.
What a fix gives you: what broke, what changed and that it works again.
Technical detail
Certificate
WE1
Security headers
A+130/100
Signed address book (DNSSEC)
Signed and validated: forged answers about where this domain lives are rejected.
Certificates issued for your names, from public Certificate Transparency logs
DNSSEC that breaks or stops validating
Certificate rules that change
Your Cyber Essentials readiness, read from your real computers and accounts – and the same results read across Cyber Essentials Plus’s tests, ISO 27001, SOC 2, NIS2, DORA and PCI DSS, so you see where the work starts (never a certificate)
Your email addresses, domain and brand, watched for breaches and lookalikes
Messages, links and websites you are unsure of – “is this a scam?” answered with every reason
What Xovris puts right
A tampered setting put back as it was – a record, a sign-in rule or a setting on your own computers you allow Xovris to fix – and put back again if it does not hold
What waits for your permission
Anything outside the zone you granted
03
Try it now,on your own.
Each of these runs in your own browser in seconds. Here is what each says for xovris.ai, checked 18 November 2026, 23:05:28 UTC – open one to run it on yours.
10 questions, each judged against the NCSC requirement it comes from, then read across Cyber Essentials Plus’s tests, ISO 27001, SOC 2, NIS2, DORA and PCI DSS.
04
What shipped for Security,strongest first.
Each one looks after this area today, with the day it shipped and the plan it starts on.
Lit: live and workingOpen: Xovris is still working on it
Xovris blocks a hostile address on your firewall itself, shown first and undone in one press
When the network watch sees an attack from outside, Xovris offers to block the address on your sensor or firewall (Suricata, FortiGate or Palo Alto): the exact change is shown first as a dry run, it is applied by Xovris on your yes, checked to prove it holds, ends by itself after the time you choose unless you keep it, and is undone in one press.
The free scam checker and your command centre now judge every message the same way
The checker on xovris.ai and Xovris’s own “is this a scam?” share one set of rules – a request to send back a code, a small fee to release a parcel, a “new number” message, a brand writing from a free mailbox – and if you already clicked, typed a password or paid, the advice now fits what you did.
Is this a scam? Give it to Xovris and find out, with every reason
Hand Xovris a message, a link or a website and Xovris tells you whether it is a scam, looks suspicious or shows no signs – never “safe” – with every reason it saw: pressure to act fast, a request for a code or a gift card, a link that hides where it goes or borrows a company’s name, a website registered days ago.
Grade your security headers from your pipeline, free
The security-headers checker now answers as an API on every plan, including Free: your site’s grade, every test behind it and the exact lines for your server, as JSON.
Cyber Essentials Plus, DORA and PCI DSS read from the same evidence
Your Cyber Essentials readiness is now also read against the five tests a Cyber Essentials Plus assessor runs, DORA’s ICT risk-management standards and PCI DSS v4.0.1 – each control counted only where your result fully stands for it, with what is still yours to do (the assessor’s own scan, PCI DSS’s stricter password rule, DORA’s incident reporting) named beside it.
Check it nowThe same first read, on the thing you are using
Try it here on yours – Xovris checks only the address you are connecting from, and only when you press.
Your router, from the internet
The doors a home or office router should keep shut, knocked on from outside on the address you are connecting from.
Xovris checks only the address this browser connects from, only when you press, and sends nothing through a door that opens.
06
Check yours,right here.
This is the same check Xovris keeps running once you keep watching. It runs in your browser now, and nothing is saved to an account.
Check yours
Read here, in your own browser. Xovris keeps nothing of it.
Questions
Does Xovris need access to my accounts to watch?
No. Watching needs nothing beyond what anyone on the internet can see. When you want Xovris to fix things, you grant access scope by scope, for as many zones and projects as you choose.
What does the free plan include?
Watching and alerts, free for good. Personal adds fixing: Xovris puts problems right, and an issue counts only once it works again.
Can I undo a fix?
Yes. Every fix has its undo written down before it runs, and a fix that fails its after-test is undone automatically.
Is my data used to train AI?
No. Your data is never used to train our AI. Your systems, files, logs and settings stay yours: they are never used to train any AI, ours or anyone else’s, and nothing of yours ever reaches another customer.
Words on this page, in plain English
Each technical word this page uses, said simply.
Plain-text data (JSON)
A common way of writing data as named values, readable by people and programs alike.
Data an app reports about itself (telemetry)
The errors, timings and records an app sends out so problems can be spotted and explained.
Email rules record (DMARC)
An address-book record telling mailboxes what to do with email that fails the domain’s sender checks – deliver it, mark it as spam or refuse it – and where to send reports.
Program-to-program connection (API, APIs)
A way for one program to ask another for information or to do something, without a person clicking through a website.
Domain Name System (DNS)
The internet’s address book: it turns a name you type into the number of the computer that answers for it.
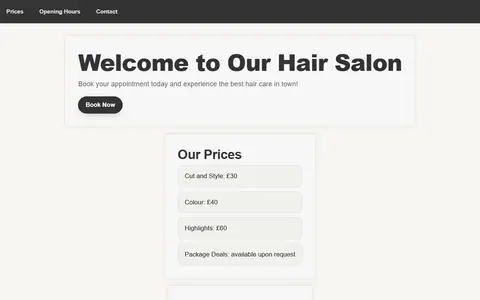 At 00:31:03 UTC
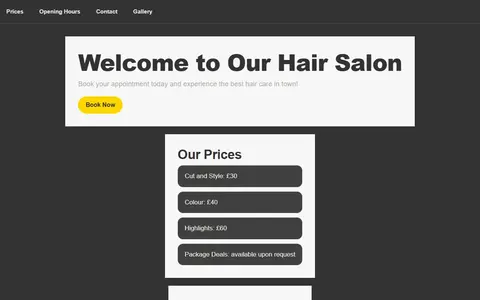 At 00:31:20 UTC